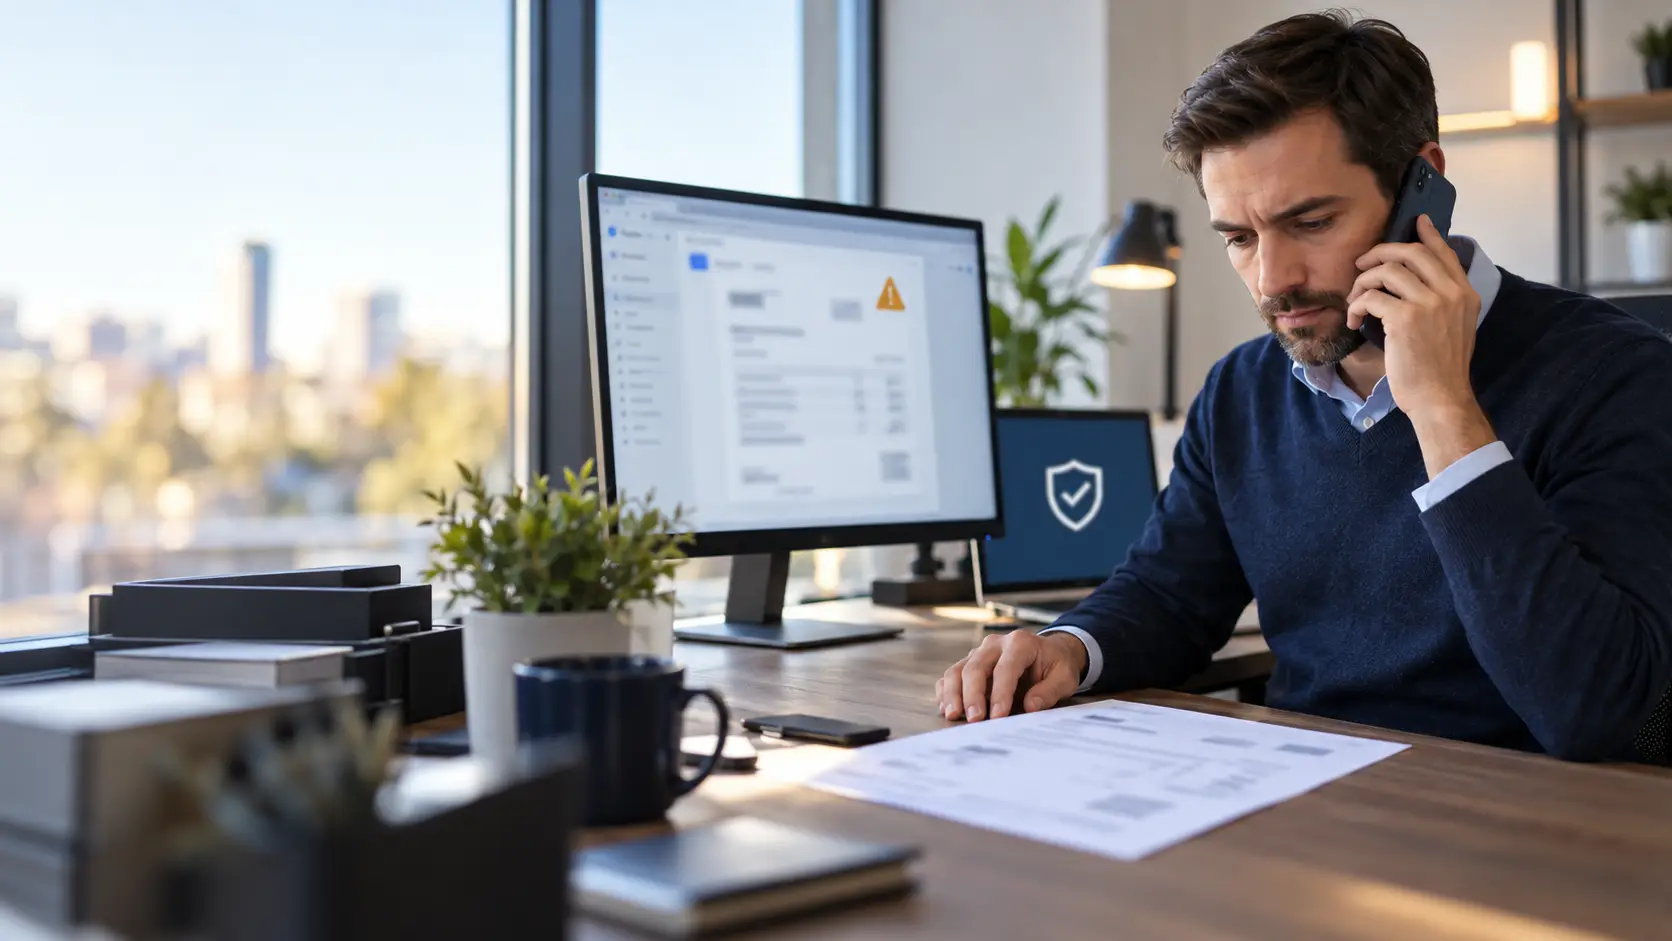
A supplier emails to say its bank details have changed. A manager asks for an urgent confidential transfer. A client receives a genuine-looking invoice from a real business, but the payment instructions lead to a criminal’s account.
These are examples of business email compromise, or BEC. The name can be misleading: the scam may involve a hacked email account, but it can also work through a lookalike address, a fake invoice or a spoofed sender (a sender identity that has been faked to make an email look like it came from someone you trust, such as a colleague, supplier or bank). In every business email compromise case, criminals exploit trust in normal business communication to redirect money, obtain sensitive information or steal goods.
INTERPOL describes BEC as a prevalent form of impersonation fraud. It says BEC was the most frequently reported fraud type in the cases and investigative-support requests it received globally, with most reports coming from the Asia-Pacific and European regions. The FBI’s IC3 recorded 24,768 BEC complaints and about US$3.05 billion in adjusted losses in 2025. These are reported figures, not a complete count of all incidents worldwide. INTERPOL 2026 Global Financial Fraud Threat Assessment, FBI IC3 2025 Annual Report
Business email compromise in South Africa
South African businesses face the same scam. SABRIC recorded R2.4 billion in digital banking crime losses in 2025, more than double the 2023 total, and that figure does not include business email compromise losses, according to ITWeb (September 2026). Fraud investigators told The Citizen that lookalike addresses often differ from the real one by a single letter or digit, and that stolen money is moved on through mule accounts within minutes.
A small test payment does not prove an account is genuine. One East Rand lodge owner told The Citizen that a R200 test payment went straight to the criminal’s account. The reliable check is to confirm new bank details with the supplier using a phone number you already had, not one taken from the email.
Who carries the loss can end up in court. In 2024 the Supreme Court of Appeal found that a firm that sent its banking details by email owed no duty of care to a non-client who paid a criminal’s account, as ITWeb reports. Stopping a business email compromise payment before it leaves is far easier than recovering it afterwards. If staff passwords or email addresses may have leaked, read our guide to dark web data scams.
How does business email compromise (BEC) happen?
A typical attack follows a chain: get information or access, learn how the business pays, send a believable request, and move the money before anyone checks.
1. Criminals learn who communicates with whom
They may study a company’s website, social media, public tenders, job listings, staff directories, supplier relationships and email formats. They look for people involved in finance, payroll, procurement, sales or executive approvals.
They may also gain useful information from a compromised supplier, employee, lawyer, property agent or client. Access to even one mailbox can reveal invoice schedules, active projects, writing styles, payment routines and the names of trusted contacts. FBI IC3 BEC overview, INTERPOL BEC guidance
2. They impersonate someone or take over a real account
There are several ways to do this:
- Phishing: A fake sign-in page or message tricks an employee into entering their password or approving a sign-in.
- Stolen or reused passwords: Criminals use credentials exposed in another breach, guessed through automated attempts, or purchased from others.
- Malware or device compromise: Malicious software can capture passwords or give an attacker access to email or other systems.
- Compromised third-party accounts: A criminal takes over a supplier’s or client’s account, then uses the real conversation to send a fraudulent invoice or bank-detail change.
- Lookalike email addresses or domains: The criminal registers an address similar to a real one, for example, with a subtle spelling or domain difference.
- Spoofed sender details: The visible sender name or address is forged to resemble a trusted contact. In this case, the real mailbox may not have been accessed at all.
So, a BEC incident does not always mean the victim business’s own email was hacked. The scam may originate from a compromised partner, an impersonating domain, or a forged sender. The FBI’s Internet Crime Complaint Center describes the same pattern: criminals compromise or spoof a trusted email account, then send a convincing request to pay or to change payment details. FBI IC3: Business email compromise
3. They keep access and quietly monitor conversations
Once inside a mailbox, an attacker may read old correspondence and wait for the right moment. They may create rules that forward or hide messages about “invoice,” “payment,” or “bank details,” so they can watch the conversation while the real user sees less of it.
They might also send messages from the compromised account, reset other passwords, access connected services, or add unauthorised recovery details. Microsoft documents malicious forwarding rules as a common feature of BEC and phishing campaigns. Microsoft: Suspicious inbox-forwarding rules
4. They send a request that fits a real business process
The request may be sent to a business, its client, its supplier, or an employee. Common scenarios include:
- Changing bank details for future supplier invoices.
- Replacing the bank account on a genuine invoice.
- Impersonating an executive and requesting an urgent, confidential transfer.
- Redirecting payroll or contractor payments.
- Interfering with a property, legal or corporate transaction.
- Asking an employee to share sensitive information or buy gift cards.
- Sending a fake invoice for services the business never ordered.
The request may arrive in an existing email thread, use a real person’s name and signature, or refer to accurate project details. Criminals may also move the conversation to a phone call, text or messaging app. The goal is to make the request feel routine enough to bypass scrutiny.
5. The money is moved quickly
After the payment reaches a criminal-controlled account, it may be moved through other accounts, payment services or cryptocurrency channels. These accounts may belong to money mules: people whose accounts are used to receive and pass on criminal funds. The longer the delay before the bank is contacted, the harder recovery can become.
What if a client pays the fake bill?
If business email compromise has already led to a payment, act immediately. Our checklist on what to do immediately after being scammed covers the first hour. Do not wait for the businesses to finish deciding who is at fault.
The client who sent the payment should:
- Call their bank’s fraud team immediately using the number on the bank card or the bank’s official website or app. Ask the bank to recall or reverse the transfer and contact the receiving bank to freeze the funds if possible.
- Tell the genuine supplier or service provider through a separately verified channel. Do not reply to the suspicious email or use the phone number in it.
- Contact the relevant police or national cybercrime-reporting service and provide the payment details, recipient account, emails, invoices, timestamps and other evidence. In South Africa, open a case at your nearest SAPS station; our guide on how to report a scam in South Africa lists the other channels.
- Preserve the evidence. Keep original emails with full headers if available, attachments, messages, bank confirmations and call records. Avoid deleting or editing them.
- Watch for recovery scams. A stranger who promises to retrieve the money for an advance fee may be targeting the victim again.
The FBI’s IC3 advises contacting the sending financial institution as soon as fraud is identified and asking for a recall or reversal. INTERPOL similarly advises immediate contact with the bank and a prompt police report. A recall is not guaranteed, but speed can matter: IC3 has described cases where funds were frozen or recalled after rapid reporting and coordination with banks. FBI IC3: BEC response steps, INTERPOL BEC guidance, IC3 2025 Annual Report: recovery examples
The business whose identity or email was used should:
- Alert its IT or email administrator immediately.
- If a mailbox may be compromised, secure it: reset credentials from a trusted device, revoke active sessions, remove unknown recovery methods and connected apps, review forwarding rules and sign-in logs, and enable MFA.
- Contact its bank if its own funds or accounts may be affected.
- Notify affected customers, suppliers and staff using a trusted channel, explaining which invoices or bank details may be fraudulent.
- Check whether other messages, accounts or payments have been altered.
- Report the incident to local law enforcement and the appropriate cybercrime or data-protection authority.
- Consider legal and regulatory advice if personal or confidential information may have been accessed.
The client’s payment does not automatically establish who is legally responsible. Liability can depend on the contract, the payment instructions, each party’s security and response, the applicable law, and the facts of the incident. Both organisations should preserve evidence and seek appropriate legal or insurance advice rather than making assumptions or deleting correspondence.
How to prevent business email compromise in your email accounts
Secure sign-ins
- Require multi-factor authentication (MFA) for all business email, especially finance, payroll, executive and administrator accounts. Use phishing-resistant MFA, passkeys or security keys where available. Our guide to MFA options for business email ranks them from strongest to weakest.
- Use unique passwords and a password manager. Don’t reuse personal passwords for work accounts.
- Remove access for former staff and review administrator privileges regularly.
- Keep devices, browsers and email software updated. Protect staff phones and laptops with screen locks and device security.
- Train staff to report unexpected sign-in prompts, password-reset notices and suspicious messages. Never approve an MFA prompt you did not initiate.
MFA can make stolen passwords less useful, but it is not a substitute for careful account monitoring and payment controls. Criminals may use social engineering to steal session access or trick people into approving prompts. CISA guidance on MFA for businesses
Watch for hidden mailbox changes
- Alert administrators to new forwarding rules, unusual sign-ins, changed recovery details and newly authorised apps.
- Restrict or monitor automatic forwarding to external email addresses.
- Ensure finance staff know how to review sent, deleted and archived messages, not just the inbox.
- Use an external-sender banner or similar indicators where available.
- Have a clear way for staff to report suspicious mail without forwarding it widely.
Make fake emails harder to send from your domain
Businesses that manage their own domains should configure and monitor SPF, DKIM and DMARC. These email-authentication controls help receiving systems check whether a message is authorised to use the business’s domain. They can reduce some forms of domain spoofing, but they do not stop an attacker from logging into a real, compromised account. Google Workspace: Email sender guidelines
How to protect clients and suppliers from business email compromise
Email security alone is not enough. Payment procedures must assume that a convincing email can be false, even when it appears inside a familiar thread.
- Verify every new or changed bank account using a trusted phone number already on file, or another established channel. Do not call a number included in the change request.
- Require a second person to approve new payment instructions and large or unusual transfers.
- For recurring suppliers, maintain a verified supplier register with known contacts and confirmed bank details.
- Use a callback process that reaches a named person, not simply whoever answers a number in the suspicious message.
- Send payment confirmations to a previously verified contact, with enough information for the recipient to identify the payment without exposing sensitive data.
- Tell clients that the business will never change bank details by email alone, if that is the company’s policy.
- Train staff to treat urgency, secrecy, pressure to bypass normal approvals, and requests to move a conversation to a new channel as warning signs.
- Limit how much personal and financial contact information is publicly available, while recognising that public information alone is not the cause of BEC.
INTERPOL and the FBI both recommend verifying bank-detail changes through a separate, trusted channel rather than replying to the email requesting the change. INTERPOL BEC guidance, FBI IC3 BEC guidance
The practical takeaway
Business email compromise succeeds when a criminal’s message is trusted as part of an ordinary business process. Sometimes the email account was genuinely compromised. Sometimes the sender only looks familiar. In either case, email should not be the sole proof that bank details have changed.
Verify payment changes independently, require dual approval for unusual transfers, and contact the bank immediately if a fake payment has already been made. Fast action may improve the chance of stopping or recovering funds; no agency or bank can guarantee that the money will be returned.
Sources
This explainer uses guidance and data from INTERPOL, the FBI IC3, CISA, Microsoft, Google, ITWeb and The Citizen. BEC terminology, reporting systems and legal obligations differ by country, so report incidents through your bank and the relevant local channels.
Business email compromise often arrives as an invoice from a supplier you have not paid before. Before you pay an unfamiliar business, run its website through our free Quick Check. For a larger amount, a Comprehensive Report looks at the business behind the website, with every finding linked to its source.
Check before you pay
About to pay a seller or business you don’t know? Start with a Free Quick Check of the advert link. It screens for common warning signs and shows where each result came from.
If you need the seller researched, a Quick Report or Comprehensive Report brings together source-linked Search Results on the seller and the offer. Neither gives a verdict: you check the sources and decide for yourself.
This article provides general security-awareness information, not legal, banking or IT advice. Recall and reporting processes differ by bank, so follow your bank’s official instructions. Sources are linked beside the claims they support and were checked in October 2026.