Old scams have not disappeared. They are familiar confidence tricks delivered through better technology. Criminals still rely on familiar emotions: fear, urgency, affection, authority, greed, embarrassment and the desire to help. What has changed is their ability to reach large audiences, personalise a story, imitate trusted people and move money across borders.
An advance-fee letter becomes a direct message from an apparent lawyer. A boiler-room investment pitch becomes a polished trading application. A call from a fake bank official gains a copied caller ID and an AI-generated voice. A forged invoice arrives inside a genuine email conversation. A romance scam uses synthetic photographs, translated messages and video filters. The story is familiar, but the supporting evidence can now be manufactured more cheaply and at greater scale.
The distinction matters because searching only for spelling mistakes, poor design or an unfamiliar accent is no longer enough. Modern fraud can be grammatically perfect, visually professional and personally relevant. A safer approach is to verify the underlying claim through a separate, trusted channel.
How old scams use new technology
Technology has affected fraud in five important ways.
Scale
Automated tools can produce and distribute messages to large numbers of potential targets. A campaign no longer needs every email, advertisement or profile to be written manually.
Personalisation
Information from data breaches, social media, public records and earlier interactions can be used to tailor a story. A message that includes a real employer, bank, purchase or family detail feels less random, even when the sender is fraudulent.
Imitation
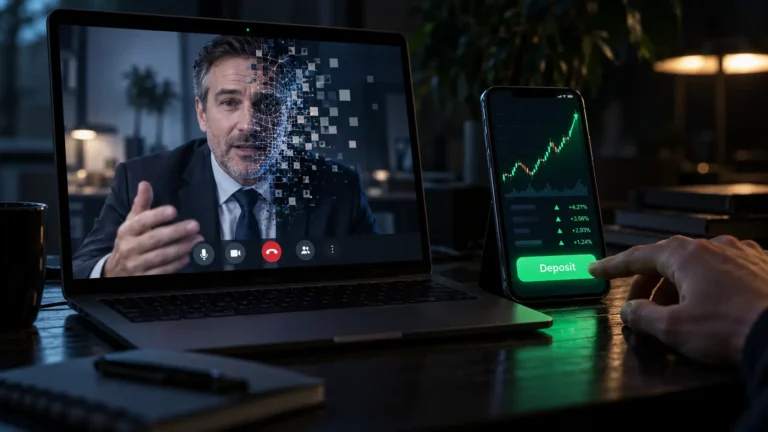
Copied websites, spoofed telephone numbers, synthetic identity documents, cloned voices and manipulated video can make an impersonation look more credible. None of these features proves that the underlying claim is true.
Coordination
Fraud is increasingly supported by specialised services. Separate participants may provide stolen data, advertisements, fake websites, scripts, call centres, compromised accounts, money mules or laundering services. Europol describes a criminal marketplace in which data and access are sold and repackaged, reducing the technical skill needed by an individual offender.
Speed
Digital payments, cryptocurrency, remote access and instant messaging allow a scheme to progress quickly. Artificial urgency is more effective when the target can act immediately without leaving the conversation.
INTERPOL’s 2026 Global Financial Fraud Threat Assessment describes the industrialisation of fraud through artificial intelligence, low-cost digital tools and international criminal collaboration. Europol likewise reports that generative AI is being used to improve social engineering and tailor approaches to a target’s personal details and cultural context.
Sources: INTERPOL, Global Financial Fraud Threat Assessment 2026 and Europol, IOCTA 2025: Steal, Deal, Repeat
1. The advance-fee scam: from letters to targeted messages
The old method is simple: a large reward is promised, but a smaller payment must be made first. Earlier versions commonly involved inheritances, lottery winnings, dormant bank accounts or funds supposedly trapped in another country.
The modern version may arrive through email, WhatsApp, social media, a dating platform or a professional networking site. The reward might be a job, loan, grant, investment withdrawal, parcel, government payment or cryptocurrency balance. The required payment is described as tax, insurance, customs duty, legal clearance, account activation or a refundable deposit.
New technology adds realistic documents, copied institutional branding and websites where a fictional balance appears to exist. AI can improve the language, translate the approach and adapt later replies to questions from the target.
The core test has not changed: independently verify the organisation, the supposed entitlement and the reason for payment. Money shown on a private dashboard is not proof that the money exists or can be withdrawn.
2. Impersonation: from uniforms and letterheads to cloned voices
Impersonation is older than electronic communication. Fraudsters have long posed as officials, bank employees, police officers, lawyers, executives or relatives. Authority encourages compliance, especially when the target is told that delay will cause financial loss, arrest, account closure or harm to another person.
Modern impersonation can combine several layers:
- a spoofed caller ID or sender name;
- a copied website and email signature;
- details collected from social media or leaked data;
- an AI-generated voice resembling a relative or executive;
- manipulated video showing an apparent official or celebrity; and
- a forged identity card, invoice or letter.
The FBI reported more than 22,000 complaints containing AI-related information in 2025, with adjusted reported losses exceeding USD 893 million. Its examples include cloned voices in distress scams, synthetic profiles in romance fraud and official-sounding messages used in business email compromise. These figures describe complaints made to the FBI, not the worldwide total, and they do not mean AI caused every loss recorded in those complaints.
Source: FBI Internet Crime Complaint Center, 2025 Annual Report
A convincing voice or video should be treated as part of the claim, not independent confirmation of it. End the contact and reach the person or institution through a number already known or obtained from an official source. For family emergencies, an agreed verification question can provide another layer of protection.
3. Phishing: from generic bait to personalised conversations
Early phishing was easy to associate with mass email: poor grammar, crude branding and a link to a copied login page. Those campaigns have not disappeared, but they now operate alongside more focused approaches delivered by text message, QR code, social advertisement, private message or search result.
Generative AI can remove obvious language errors, create many variations and continue a plausible conversation. Stolen information may allow a message to mention the recipient’s bank, employer, service provider or recent activity. A phishing page can also be placed behind an advertisement or QR code so that the destination is not visible until the link is opened.
South Africa’s SABRIC reported that digital-banking fraud remained the dominant channel in its 2024 member statistics. It also identified AI-written phishing and WhatsApp messages and early voice-cloning cases, while emphasising that social engineering exploited human behaviour rather than technically compromising bank platforms.
Source: SABRIC, Annual Crime Statistics 2024
The durable protection is not the ability to recognise bad writing. It is refusing to sign in, disclose credentials or approve an action through an unsolicited contact. Open the official application or enter the known website address independently.
4. Romance and friendship scams: from correspondence to synthetic identities
Romance fraud traditionally required patience. The offender created a relationship, introduced a crisis and requested financial help. The same structure remains: attention builds trust, distance explains why the parties cannot meet and an emergency or opportunity turns affection into payment.
New tools make the identity easier to construct and maintain. Images can be stolen or generated. Translation and conversational AI help an operator communicate with more targets. Video can be manipulated, while prerecorded clips and connectivity problems can be used to explain why a live conversation is limited. Separate operators may even work from a shared script or account.
Some schemes gradually introduce an investment platform. The relationship supplies trust, while a fake account displays profits. The victim is then encouraged to deposit increasingly large amounts. This combination is sometimes called relationship investment fraud; the emotional and financial elements reinforce each other.
The warning is not that every online relationship is false. It is that affection cannot authenticate an investment, identity or payment request. Reverse-image searches, independent identity checks and live conversations can supply useful context, but none is conclusive alone. Refusal to meet, repeated emergencies, pressure to invest and requests involving third-party accounts should be examined together.
5. Investment fraud: from boiler rooms to fake trading platforms
Boiler-room operations have long used persistent salespeople to promote worthless or non-existent investments. Modern versions retain the script but add online advertisements, messaging groups, remote onboarding and convincing dashboards.
A victim may see a celebrity endorsement, financial-news interview or social-media success story and follow a link to a platform. The interface shows growing returns, and an “account manager” encourages additional deposits. Sometimes a small withdrawal is allowed to strengthen confidence. When a larger withdrawal is requested, new taxes, verification fees or liquidity payments appear.
Deepfake video and cloned audio can place familiar faces inside fabricated promotions. The FSCA has identified deepfake advertisements, impersonation of authorised entities, social-media scams, copy-trading offers and unregulated online trading among current concerns. A genuine company’s name or licence number may be copied, so confirming that a business exists is only the beginning.
Source: FSCA, Regulatory Actions Report to 30 June 2025
Verify the exact legal entity, regulatory authorisation, website, representative and payment beneficiary through independently obtained details. A video endorsement, account balance or group of enthusiastic participants does not demonstrate that assets were actually purchased.
6. Business email compromise: from forged instructions to hijacked conversations
Payment-diversion fraud once depended largely on forged letters, faxed instructions or lookalike email addresses. It now frequently uses compromised email accounts and detailed knowledge of an organisation’s normal activity.
A criminal can monitor correspondence until an invoice, property payment, supplier settlement or payroll instruction is expected. New bank details are then inserted into the conversation. Because the surrounding messages and attachment may be genuine, the request can be difficult to distinguish visually.
AI can produce an executive’s tone, translate messages and create polished instructions quickly. Voice cloning can add a telephone call that appears to confirm the payment. The FBI’s 2025 report says businesses reported more than USD 30 million in losses from business email compromise complaints with an AI nexus during that year, while noting that many BEC methods do not require AI.
The most reliable defence is procedural: confirm every new or changed beneficiary through a separate, trusted channel. Use a telephone number already held on file, not the number contained in the change request. Higher-value payments should require more than one approval.
7. Fake shops and counterfeit offers: from street stalls to disposable storefronts
Misrepresentation in retail is not new. What has changed is the speed with which a convincing store can be created, advertised and abandoned. A fake shop can copy photographs, product descriptions, policies and reviews from legitimate businesses. Social advertising allows it to reach a defined audience, while instant payment can move funds before complaints accumulate.
Marketplace scams use a similar pattern without a full website. An attractive product is offered below market value, a deposit is requested and collection or delivery never occurs. The seller’s profile may be compromised, recently created or supported by stolen identity information.
Modern storefronts can look better than genuine small-business sites. Design quality is therefore a weak test. Stronger questions include:
- Which legal entity is selling the product?
- Does the payment beneficiary match that entity or have a credible explanation?
- Do the address and contact details exist outside the seller’s own pages?
- How old is the domain, and what did it previously contain?
- Are the returns and refund terms coherent?
- Are independent reviews distributed over time?
- Does the payment method provide a realistic dispute process?
One inconsistency may have an innocent explanation. Several connected inconsistencies deserve closer investigation.
8. Technical-support fraud: from alarming calls to remote control
The traditional technical-support scam tells the target that a computer is infected and demands payment for unnecessary repairs. Modern versions may impersonate a bank, mobile provider, software company or fraud investigator and direct the target to install a legitimate remote-access application.
Once access is granted, the operator may view the screen, collect information, alter what the user sees or guide the user through a transaction. Malicious remote-access tools can provide even broader control. A bank login performed while an unknown person can observe or control the device exposes more than the single transaction being discussed.
The method works because remote-support software also has legitimate uses. The risk lies in who initiated the session, how their identity was verified and what access was granted. An unsolicited caller should not be allowed to control a device. If access has already been provided, disconnect the device, contact affected institutions from another trusted device and obtain qualified technical help.
9. Money-mule recruitment: from cash couriers to digital accounts
Criminal networks need ways to receive and move money. Traditionally, this might involve cash couriers, forged cheques or accounts opened under false identities. Digital fraud also relies on people who receive funds into bank accounts, payment applications or cryptocurrency wallets and then forward or withdraw them.
Recruitment may be disguised as employment, payment processing, investment, romance or a favour for someone who claims to be unable to access an account. The participant is offered commission for allowing money to pass through a personal or business account.
Technology has widened the pool of potential recruits and accelerated transfers, but the central role remains the same: the mule separates the victim’s payment from the organisers. The person moving the money can face serious legal and financial consequences even if they did not design the original scam.
An employer or customer should not need unexplained access to a worker’s personal bank account. Requests to receive, convert or forward money for strangers should be treated as a significant warning sign.
10. Recovery fraud: the old second scam with better targeting
Recovery fraud targets people who have already lost money. The operator claims to be a lawyer, regulator, investigator, bank employee, hacker or recovery specialist and promises to retrieve the loss for an upfront payment.
The modern version can be highly specific because the criminal already has details of the original transaction. Victim lists may be retained, shared or sold. The approach can quote the platform used, amount lost and names involved. A professional website and fabricated recovery documents make the service appear credible.
The FBI recorded 10,516 recovery-scam complaints associated with USD 1.4 billion in reported losses during 2025, while cautioning that some complainants may have included their original fraud loss in that amount. The figures still demonstrate the scale of repeated targeting.
Legitimate investigators and legal representatives should be independently verified. A person who unexpectedly knows about the loss may have obtained that information from the original network rather than from an official case.
Why familiar warning signs are becoming less reliable
Advice about spelling errors, crude logos and implausible stories remains useful for low-effort scams, but it does not address the strongest modern impersonations. Criminals can copy authentic material, automate corrections and adapt in real time.
Several commonly trusted signals have weakened:
- A local telephone number: caller ID can be spoofed or obtained remotely.
- A familiar voice: audio can be cloned or replayed.
- A live-looking video: video may be manipulated, prerecorded or presented through a filter.
- A professional website: templates, copied content and AI-generated material are widely available.
- A company registration: real company details can be copied by an impersonator.
- A regulator’s licence number: the number may belong to a legitimate entity that is not involved.
- Positive reviews: reviews can be fabricated, purchased or imported from another business.
- Personal knowledge: the information may come from social media, a data breach or an earlier compromise.
These clues still contribute evidence. They simply should not carry the entire decision.
A verification method that survives new technology
The strongest response to persuasive media is procedural verification. Instead of asking only whether the message looks real, test whether the claim survives outside the communication controlled by the sender.
Pause the requested action
Urgency narrows attention. A short pause creates time to inspect the claim, consult another person and choose an independent contact route. Legitimate organisations generally have procedures for customers who end a call and reconnect securely.
Separate the claim from its supporting performance
A voice, video, document or dashboard may be impressive without proving the underlying facts. Write down the actual claim: who is contacting you, what happened, what action is required and where the money or information will go.
Rebuild contact independently
Use a saved number, official application, number printed on a card, regulator’s register or website address entered independently. Do not use the contact details, search advertisement or link supplied in the suspicious conversation.
Verify the transaction, not only the person
Even a genuine account may be compromised. Confirm the beneficiary, amount, purpose and any changed instructions. For investments, establish who holds the assets and which regulated entity is responsible. For online purchases, identify the contracting seller and the applicable refund process.
Compare several independent sources
Company records, regulator notices, domain history, archived pages, addresses, connected accounts and public reporting can reveal contradictions. No single database proves safety. Agreement across genuinely independent sources is more useful than repeated claims originating from the same website.
Preserve evidence
Save full URLs, messages, advertisements, invoices, email headers, payment records, telephone numbers and screenshots. Record the sequence of events. Pages and profiles can disappear quickly after a campaign is exposed.
The central lesson
Fraud has not evolved by replacing human psychology. It has evolved by making manipulation easier to produce, personalise and distribute.
The old request is still there: trust me, act now, keep this private, send the money or give me access. New technology supplies a more convincing person, document, website or explanation around that request.
This is why verification should not depend on spotting an artificial voice or identifying an AI-generated image. Detection tools can help, but ordinary people should not be expected to win a technical contest against every new form of synthetic media. The safer standard is independent confirmation: leave the channel controlled by the claimant and test the important facts elsewhere.
What an AdUncovered report can and cannot establish
AdUncovered researches the seller or business behind an offer using available public information. Reports address your questions, highlight material warning signs and compare relevant claims with the evidence found. Customer complaints are distinguished from established facts, and conflicting or unavailable information is clearly explained.
Choose a Quick Report for a focused seller check covering serious warnings, scam reports, customer complaints and reviews, and the advert versus the published offer. Ordinary research covers the past year. Quick does not investigate your individual transaction or prepare a refund claim.
Choose a Comprehensive Report for broader research across the main concern areas, normally covering the past three years. Where supplied, it also examines your transaction details and relevant refund-related information. Research concerns one identified seller or business and its connected shops, websites and accounts.
Relevant court orders and trading restrictions have no age cutoff in either report. We include other material concerns discovered within the selected scope, not only those you selected.
Provide a usable public link identifying the seller, shop, profile, listing or offer, together with the relevant details in writing. A business does not need its own website, but we need enough public information to investigate the correct seller.
Neither report guarantees safety, determines criminal guilt, provides legal advice or recovers money. No negative findings does not establish that an offer is safe: records may be incomplete, publication may be delayed and new information may appear after the research date.
For a closer look at the organisations and service providers behind large campaigns, read How Scam Networks Operate: Known Hubs, Methods and Specialisations.
Research limitations
This article describes documented patterns and does not suggest that every use of AI, remote-access software, cryptocurrency, online dating or social media is suspicious. These technologies have extensive legitimate uses. Risk depends on the surrounding conduct, identity verification, transaction and evidence.
Complaint statistics are also incomplete. They reflect the jurisdiction, definitions and reporting system of the organisation collecting them. Many incidents are never reported, while one complaint can involve several techniques. Figures from the FBI, INTERPOL, Europol, SABRIC and the FSCA should therefore be read as evidence of patterns rather than a complete count of global fraud.
Principal sources
- INTERPOL, Global Financial Fraud Threat Assessment 2026
- INTERPOL, Report warns of increasingly sophisticated global financial fraud
- Europol, IOCTA 2025: Steal, Deal, Repeat
- Europol, Online Fraud Schemes: A Web of Deceit
- FBI Internet Crime Complaint Center, 2025 Annual Report
- FBI, Criminals Use Generative AI to Facilitate Financial Fraud
- SABRIC, Annual Crime Statistics 2024
- FSCA, Regulatory Actions Report to 30 June 2025
Editorial note: This article provides general public-source research and practical guidance. It is not legal, financial or law-enforcement advice. The presence of a warning sign does not by itself establish wrongdoing, and its absence does not establish safety.
Check before you pay
About to pay a seller or business you don’t know? Start with a Free Quick Check of the advert link. It screens for common warning signs and shows where each result came from.
If you need the seller researched, a Quick Report or Comprehensive Report brings together source-linked Search Results on the seller and the offer. Neither gives a verdict: you check the sources and decide for yourself.